



Information policy and security
In 2025, KEGOC JSC consistently implemented its Information Policy based on the principles of transparency, reliability, completeness, consistency and timely disclosure of information. The Company provided equal access to material information for all categories of stakeholders in accordance with the requirements of the legislation of the Republic of Kazakhstan, KASE and AIX rules, and internal corporate documents.
Timely and correct disclosure of information contributed to strengthening trust among investors, partners, service consumers and society as a whole, as well as maintaining the Company’s investment attractiveness.
KEGOC JSC strictly complies with legal requirements regarding the protection of commercial, official and confidential information. Information security matters are integrated into all processes for preparing, agreeing and disseminating corporate data. When disclosing information, a balance is maintained between transparency and protection of sensitive information.
Information security
SASB IF-EU-550a.1
KEGOC JSC applies a zero-tolerance policy towards violations of information security requirements. Persons who violate the Information Security Policy or other regulatory documents in this area are subject to disciplinary or other liability in accordance with the legislation of the Republic of Kazakhstan and the Company’s internal regulations.
The Company has a formalized process for identifying, recording, investigating and eliminating violations of information security requirements and personal data processing. An investigation is initiated upon receipt of information about a possible violation, including appeals from data subjects, internal employee notifications, monitoring results, audits or information security incidents. All appeals and incidents are registered in the prescribed manner.
The Security Department conducts a preliminary assessment of an incident, determining the nature of the violation, affected data, potential risks and need for escalation. As part of the investigation, system logs and user actions are analyzed, compliance with the Privacy Policy is checked, and the causes of the incident and responsible persons are identified. Based on the investigation results, a report is prepared and corrective measures are implemented, including elimination of identified violations, updating procedures and technical controls, additional staff training and, where necessary, application of disciplinary measures.
Where necessary, the Company notifies management, personal data subjects and regulatory authorities in accordance with legal and internal policy requirements.
Information Security Management System
The main objective of information security activities is to ensure the protection of information assets of KEGOC JSC, as well as to coordinate and develop information security processes.
Information security management is integrated into the Company’s corporate risk management system and is considered one of the factors ensuring the resilience and reliability of energy infrastructure operation.
The Information Security Management System (ISMS) has been developed and implemented based on the international standard ISO/IEC 27001 and is part of the Company’s integrated management system. The scope of the ISMS is the information system for managing processes of the financial and economic block, supporting the implementation of core and auxiliary business processes.
To comply with the standard, the Information Security Policy was approved and regulations on information asset management were implemented. In 2025, the Company continued improving measures to ensure the security of information assets.
KEGOC JSC annually undergoes internal and external audits of the information security management system for compliance with ISO 27001. Based on the external audit, the Company’s compliance with the standard was confirmed and an ISO 27001 certificate was obtained.
Monitoring and protection of information systems
During 2025, information security systems operated steadily. The Company continuously monitored the security of information systems, which made it possible to identify and prevent cyber threats in a timely manner.
Information protection systems detect and block malicious software, including ransomware, and prevent the spread of spam and phishing messages. To improve the security of remote work, two-factor authentication is used when connecting to the corporate network.
Together with the Operational Information Security Centre of QazCloud LLP, round-the-clock monitoring and response to information security events is carried out. As part of this cooperation, quarterly scanning of the information and communication infrastructure for vulnerabilities, as well as penetration testing, is conducted. Based on these activities, recommendations are provided to improve the protection of the Company’s information systems.
To assess the effectiveness of the information security system, the Company also uses incident monitoring indicators, penetration testing results and data on identified vulnerabilities of information systems.
In the reporting year, no serious information security incidents resulting in financial or reputational losses were recorded.
Information security incident management
KEGOC JSC has an information security incident management system that determines the procedure for actions in the event of cyber incidents and other threats to the Company’s information systems.
The main objective of incident management is to minimize possible damage, promptly restore normal operation of information systems and prevent repeated incidents.
Company employees are required to immediately report any events that pose a threat to information security, as well as identified vulnerabilities. Users are prohibited from independently checking or eliminating vulnerabilities to prevent additional risks.
If malicious software infection is suspected, employees must immediately notify authorized specialists.
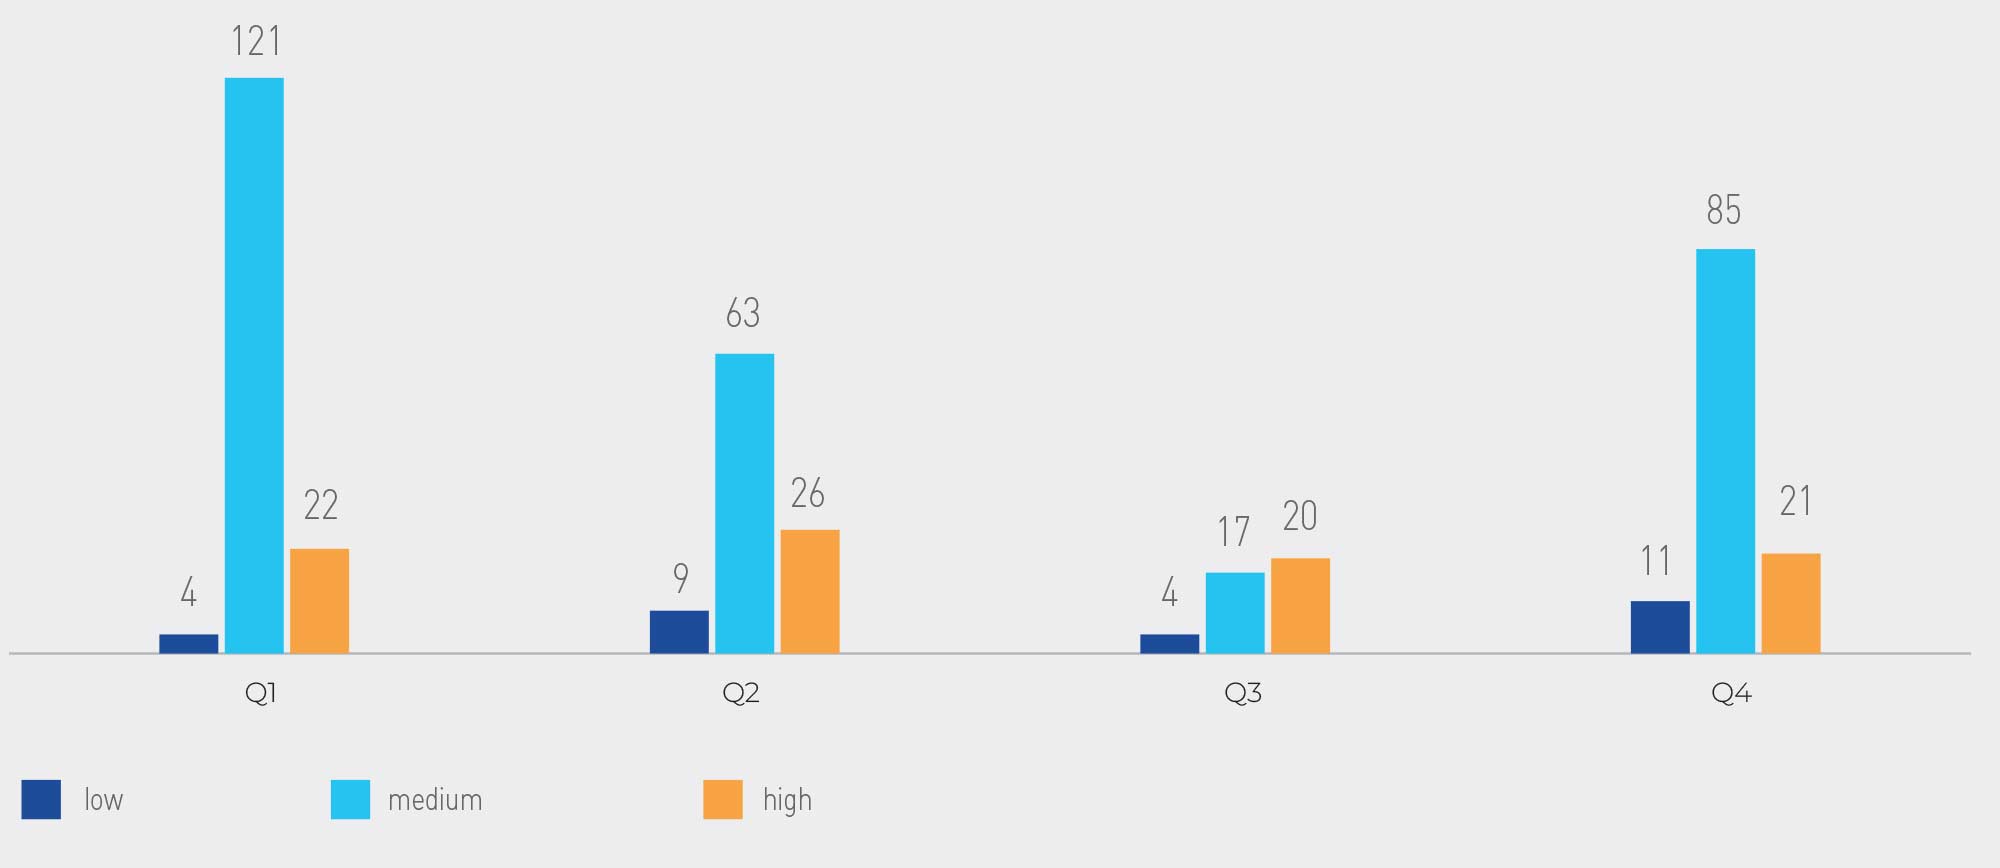
In 2025, KEGOC JSC registered 438 information security incidents. The largest number of events related to malicious software detected on users’ workstations.
Distribution of information security events by quarter in 2025
Emergency Preparedness
The Company has business continuity procedures aimed at minimizing the impact of internal and external factors on the functioning of information systems.
In accordance with the Information Infrastructure Business Continuity Plan, annual testing of system readiness for recovery after possible information security incidents is conducted.
Internal and External Audit
KEGOC JSC regularly conducts internal and external audits of the information security management system. Audits are aimed at assessing the effectiveness of system processes, identifying weaknesses and determining areas for further improvement.
In addition, in accordance with legal requirements, external penetration testing is conducted annually.
Risk Management
Information security risk management is part of the corporate risk management system of KEGOC JSC.
Risk assessment is conducted in relation to the Company’s information assets. Based on the assessment results, a report on the risk level and an action plan for reducing risks are prepared.
The Company applies a risk-oriented approach to information security management, ensuring systematic identification, assessment and management of cyber risks across the organization.
The Company continuously improves risk management processes and information security measures, taking into account international practices and technological development.
Raising Employee Awareness
KEGOC JSC pays attention to forming a culture of responsible attitude to information security among employees.
In 2025, training activities were conducted on cyber hygiene and compliance with Information Security Policy requirements. Employee testing was conducted to assess training effectiveness.
Special attention is paid to onboarding new employees. Upon hiring, employees undergo mandatory induction briefing on information security. In 2025, 32 new employees completed this briefing.
A pilot information security training platform with simulated phishing attack of users was also conducted. Based on the results of the training attack, no employees susceptible to phishing were identified.
Protection of Confidential Information
All employees of KEGOC JSC sign a non-disclosure obligation for confidential information upon hiring and undergo relevant briefing.
Confidentiality requirements are also included in contracts with suppliers and partners, which ensures the protection of the Company’s information when interacting with external counterparties.
Compliance with the Privacy and Personal Data Processing Policy is also assessed as part of the annual external audit of the information security management system.